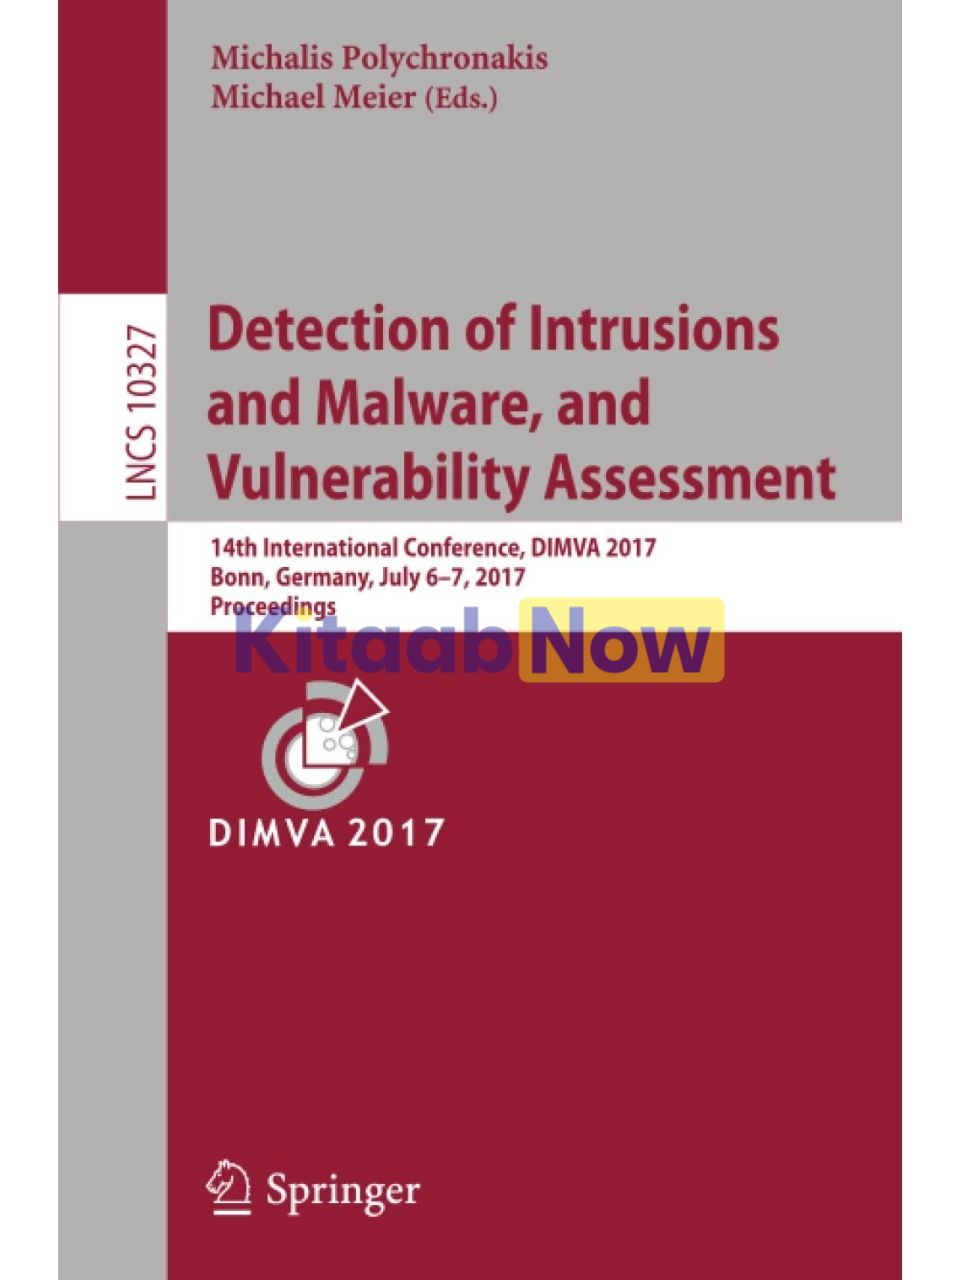
Detection of Intrusions and Malware, and Vulnerability Assessment: 14th International Conference, DIMVA 2017, Bonn, Germany, July 6-7, 2017, Proceedings
Rs. 20,985
- Edited By: Michalis Polychronakis, Michael Meier
- ISBN: 9783319608754
- Publisher: Springer Publishing Company
- Publication Date: June 4, 2017
- Format: Paperback – 412 pages
- Language: English
Out of stock
Share
Description
This book constitutes the refereed proceedings of the 14th International Conference on Detection of Intrusions and Malware, and Vulnerability Assessment, DIMVA 2017, held in Bonn, Germany, in July 2017.
The 18 revised full papers included in this book were carefully reviewed and selected from 67 submissions. They present topics such as enclaves and isolation; malware analysis; cyber-physical systems; detection and protection; code analysis; and web security.
Table of Contents
- Enclaves and Isolation
- Malware Guard Extension: Using SGX to Conceal Cache Attacks – Michael Schwarz, Samuel Weiser, Daniel Gruss, Clémentine Maurice, Stefan Mangard
- On the Trade-Offs in Oblivious Execution Techniques – Shruti Tople, Prateek Saxena
- MemPatrol: Reliable Sideline Integrity Monitoring for High-Performance Systems – Myoung Jin Nam, Wonhong Nam, Jin-Young Choi, Periklis Akritidis
- Malware Analysis
- Measuring and Defeating Anti-Instrumentation-Equipped Malware – Mario Polino, Andrea Continella, Sebastiano Mariani, Stefano D’Alessio, Lorenzo Fontana, Fabio Gritti et al.
- DynODet: Detecting Dynamic Obfuscation in Malware – Danny Kim, Amir Majlesi-Kupaei, Julien Roy, Kapil Anand, Khaled ElWazeer, Daniel Buettner et al.
- Finding the Needle: A Study of the PE32 Rich Header and Respective Malware Triage – George D. Webster, Bojan Kolosnjaji, Christian von Pentz, Julian Kirsch, Zachary D. Hanif, Apostolis Zarras et al.
- Cyber-physical Systems
- Last Line of Defense: A Novel IDS Approach Against Advanced Threats in Industrial Control Systems – Mark Luchs, Christian Doerr
- LED-it-GO: Leaking (A Lot of) Data from Air-Gapped Computers via the (Small) Hard Drive LED – Mordechai Guri, Boris Zadov, Yuval Elovici
- A Stealth, Selective, Link-Layer Denial-of-Service Attack Against Automotive Networks – Andrea Palanca, Eric Evenchick, Federico Maggi, Stefano Zanero
- Detection and Protection
- Quincy: Detecting Host-Based Code Injection Attacks in Memory Dumps – Thomas Barabosch, Niklas Bergmann, Adrian Dombeck, Elmar Padilla
- SPEAKER: Split-Phase Execution of Application Containers – Lingguang Lei, Jianhua Sun, Kun Sun, Chris Shenefiel, Rui Ma, Yuewu Wang et al.
- Deep Ground Truth Analysis of Current Android Malware – Fengguo Wei, Yuping Li, Sankardas Roy, Xinming Ou, Wu Zhou
- Code Analysis
- HumIDIFy: A Tool for Hidden Functionality Detection in Firmware – Sam L. Thomas, Flavio D. Garcia, Tom Chothia
- BinShape: Scalable and Robust Binary Library Function Identification Using Function Shape – Paria Shirani, Lingyu Wang, Mourad Debbabi
- Web Security
- On the Privacy Impacts of Publicly Leaked Password Databases – Olivier Heen, Christoph Neumann
- Unsupervised Detection of APT C&C Channels using Web Request Graphs – Pavlos Lamprakis, Ruggiero Dargenio, David Gugelmann, Vincent Lenders, Markus Happe, Laurent Vanbever
- Measuring Network Reputation in the Ad-Bidding Process – Yizheng Chen, Yacin Nadji, Rosa Romero-Gómez, Manos Antonakakis, David Dagon
Editors Biography
Michalis Polychronakis
Stony Brook University, Stony Brook, USA
Michael Meier
University of Bonn and Fraunhofer FKIE, Bonn, Germany
Additional information
| Weight | 0.646 kg |
|---|
Only logged in customers who have purchased this product may leave a review.
Related Products


Reviews
There are no reviews yet.